 1 hour ago
12
TLDR
- Revolut confirmed a data breach affecting about 680 customers after fraudulent requests were sent from a hacked government agency email domain.
- Exposed data may include names, addresses, ID documents, selfies, IBANs, and Bitcoin transaction details for crypto customers.
- A group calling itself Revolut Smilik claims responsibility and is demanding 10,000 Bitcoin, threatening to leak more files daily.
- The UK Financial Conduct Authority is reviewing the incident, and Revolut says no funds or systems were compromised.
- Former Mt. Gox CEO Mark Karpelès and crypto figure Marc Zeller are among those confirmed affected.
Revolut has confirmed a data breach that has affected roughly 680 customers. The company disclosed the incident on September 12, 2026.
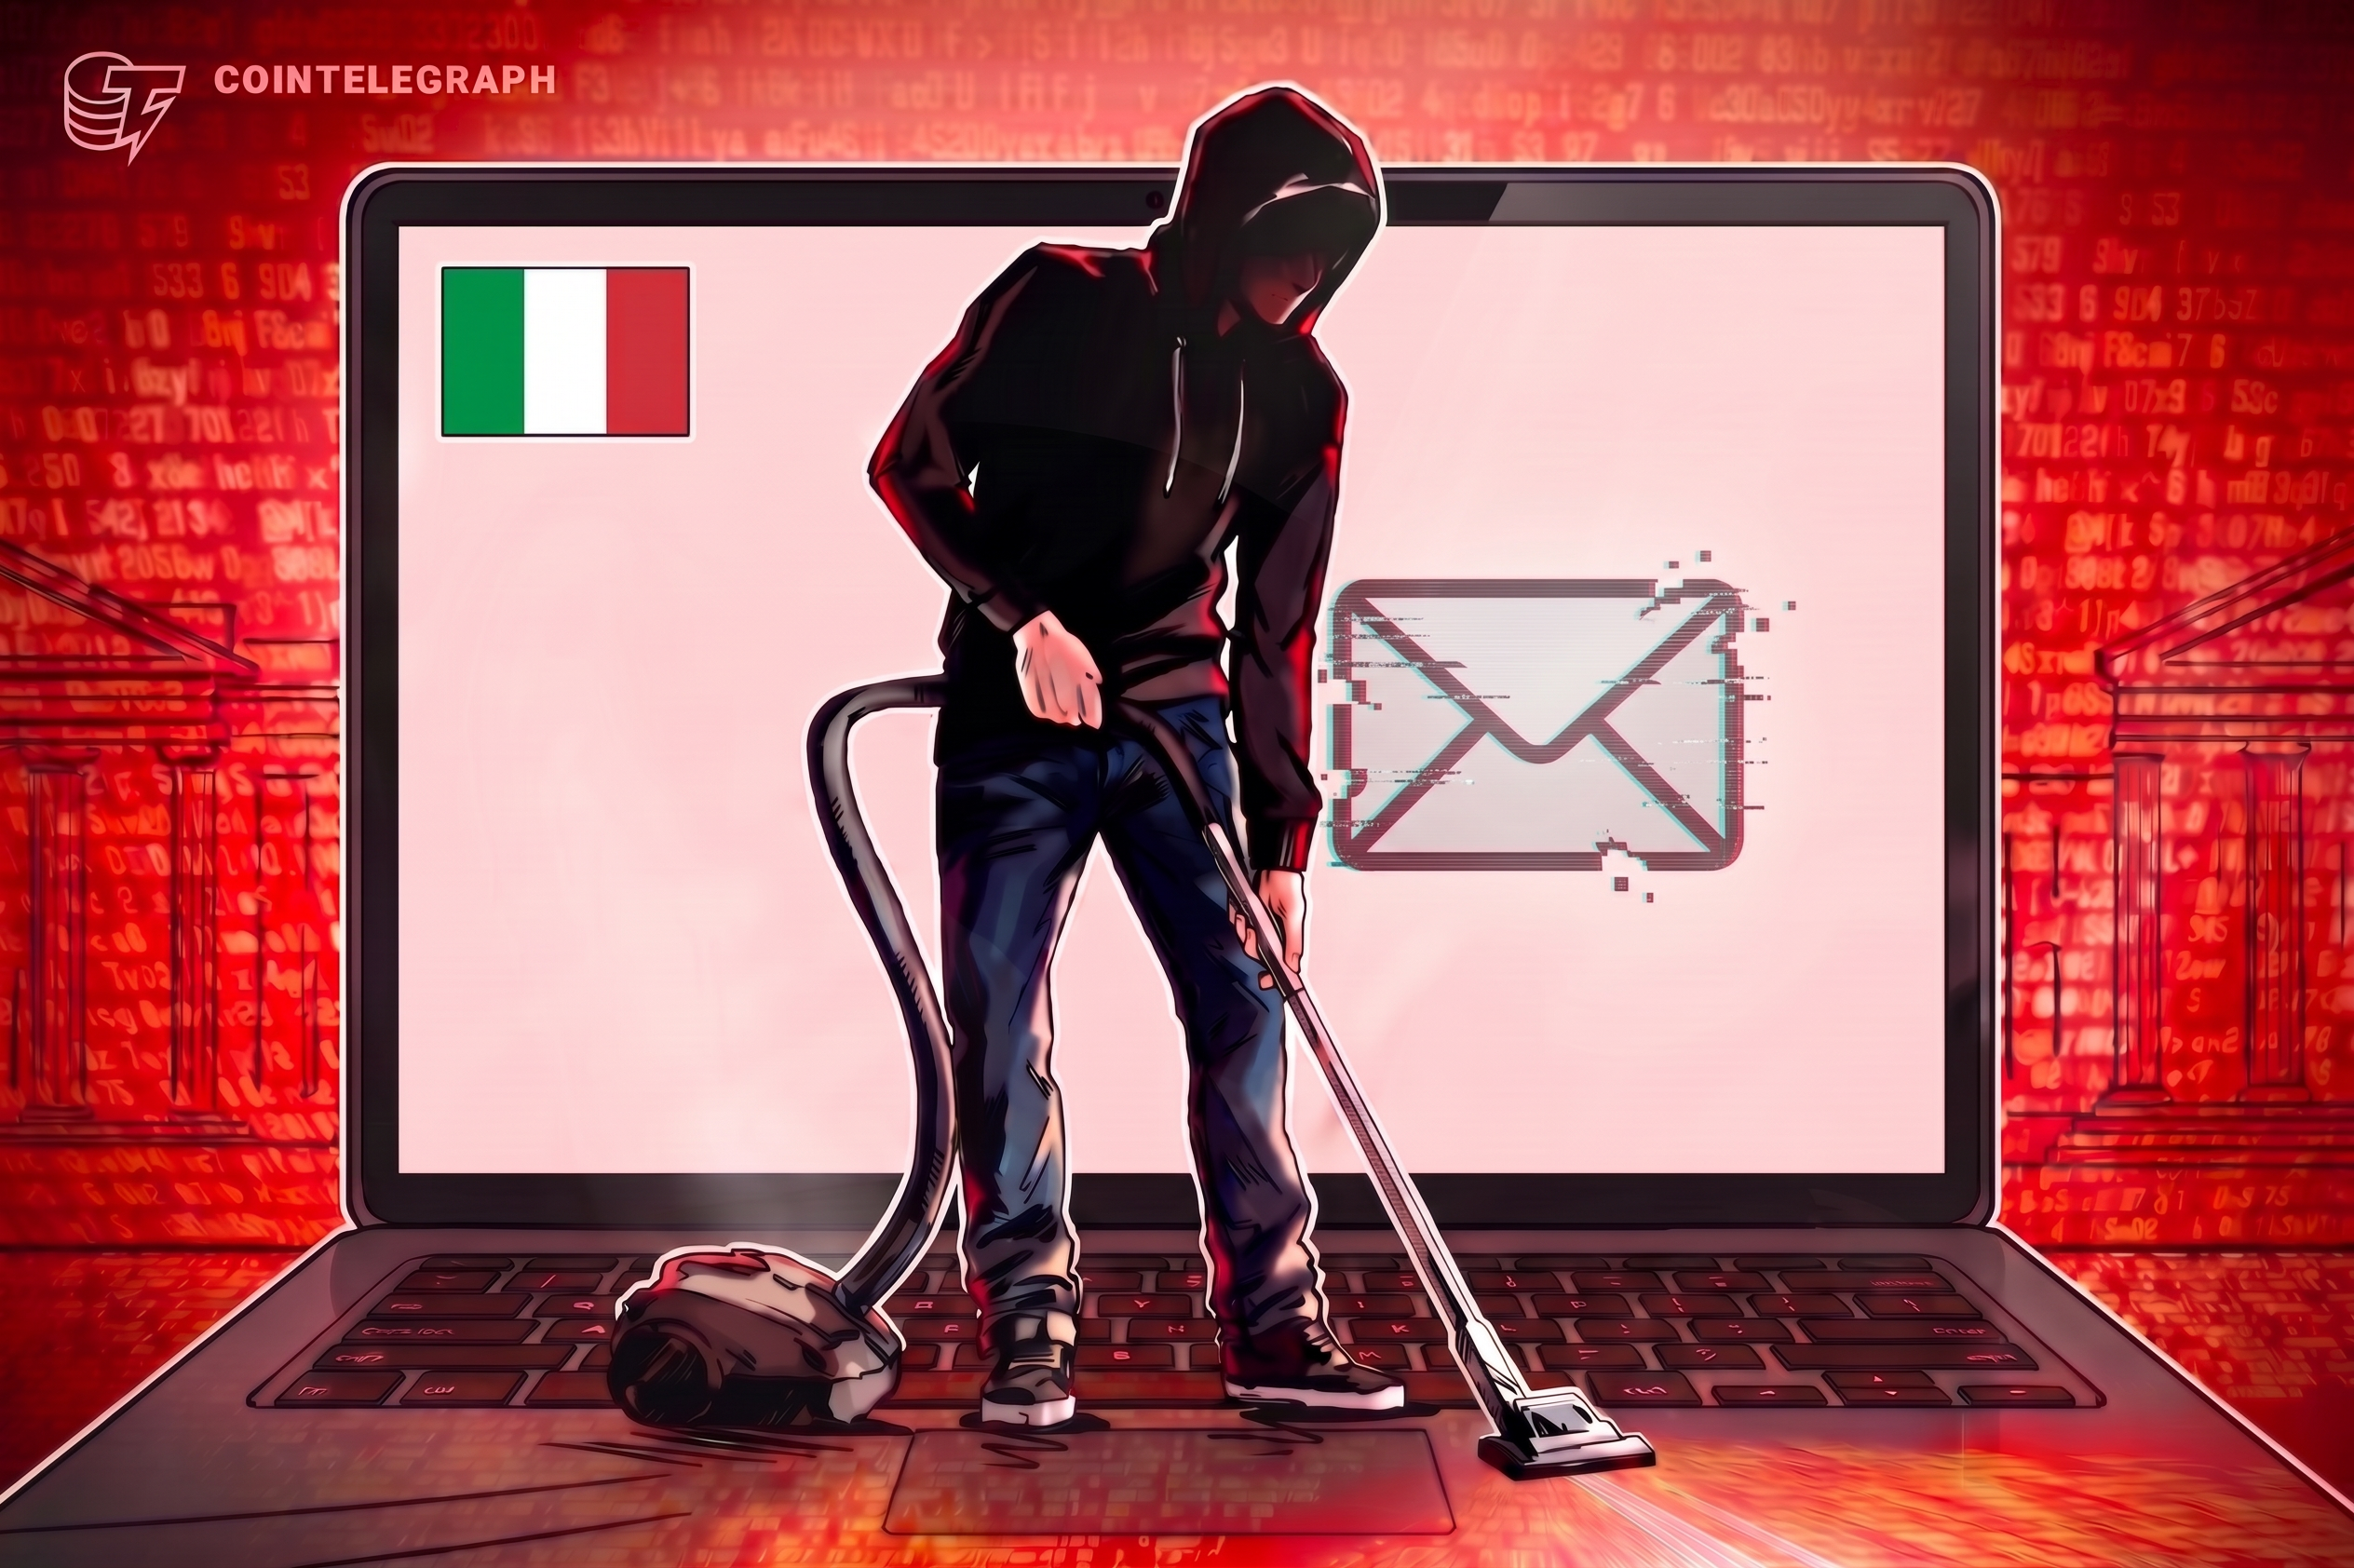
The breach did not come from a direct hack of Revolut’s systems. Instead, attackers used a compromised government agency email domain to send what looked like legitimate data requests.
Revolut’s compliance team processed the requests as authentic. The messages carried valid credentials that made the domain appear trustworthy. The company later called it a “sophisticated external impersonation scam.”
What Information Was Exposed
The exposed data may include names, dates of birth, occupations, addresses, emails, and phone numbers. Passport or driver’s license images and identity verification selfies may also be included.
Revolut said biometric facial telemetry data was not exposed. Financial details that may have been shared include IBANs, account opening dates, account status, and transactino history.
For crypto account holders, Bitcoin transaction records and wallet reference numbers may have been part of the leaked data. Private keys and full card numbers were not included.
Former Mt. Gox CEO Mark Karpelès said he received a warning email from Revolut at 5:25 a.m. on September 12. Crypto entrepreneur Marc Zeller also confirmed his information was affected.
Regulators and Hackers Respond
The UK Financial Conduct Authority has started reviewing the breach and is in contact with Revolut. The company says it blocked the fraudulent IP address once the scam was discovered.
Revolut reported the matter to law enforcement, data protection authorities, and financial regulators. A company spokesperson said customer funds and internal systems were not affected.
A group calling itself Revolut Smilik has taken credit for the attack. The group is demanding 10,000 Bitcoin and has threatened to release stolen files daily if the demand is not met.
Revolut has not said whether it received or responded to the ransom demand. Materials tied to the breach were shared on a Telegram channel, which has since been shut down.
On-chain investigator ZachXBT said the breach appears small in scale and may have targeted high-net-worth customers specifically. Some details from the Telegram posts remain unverified.
Reports indicate the compromised government email may have come from an Italian domain. Italian authorities have not responded to requests for comment.
The FBI has previously warned that criminals sometimes gain access to government or law enforcement email accounts to send fake emergency data requests. These messages can appear legitimate because they come from trusted domains.
The breach comes months after Revolut received approval to operate a UK bank. Crypto holdings are not covered under UK deposit protection rules that apply to standard banking deposits.
Revolut serves more than 80 million customers worldwide. The company says it has contacted all affected customers directly, and the investigation into the breach is ongoing.
The post Revolut Confirms Data Breach Affecting 680 Customers appeared first on Blockonomi.



 English (US) ·