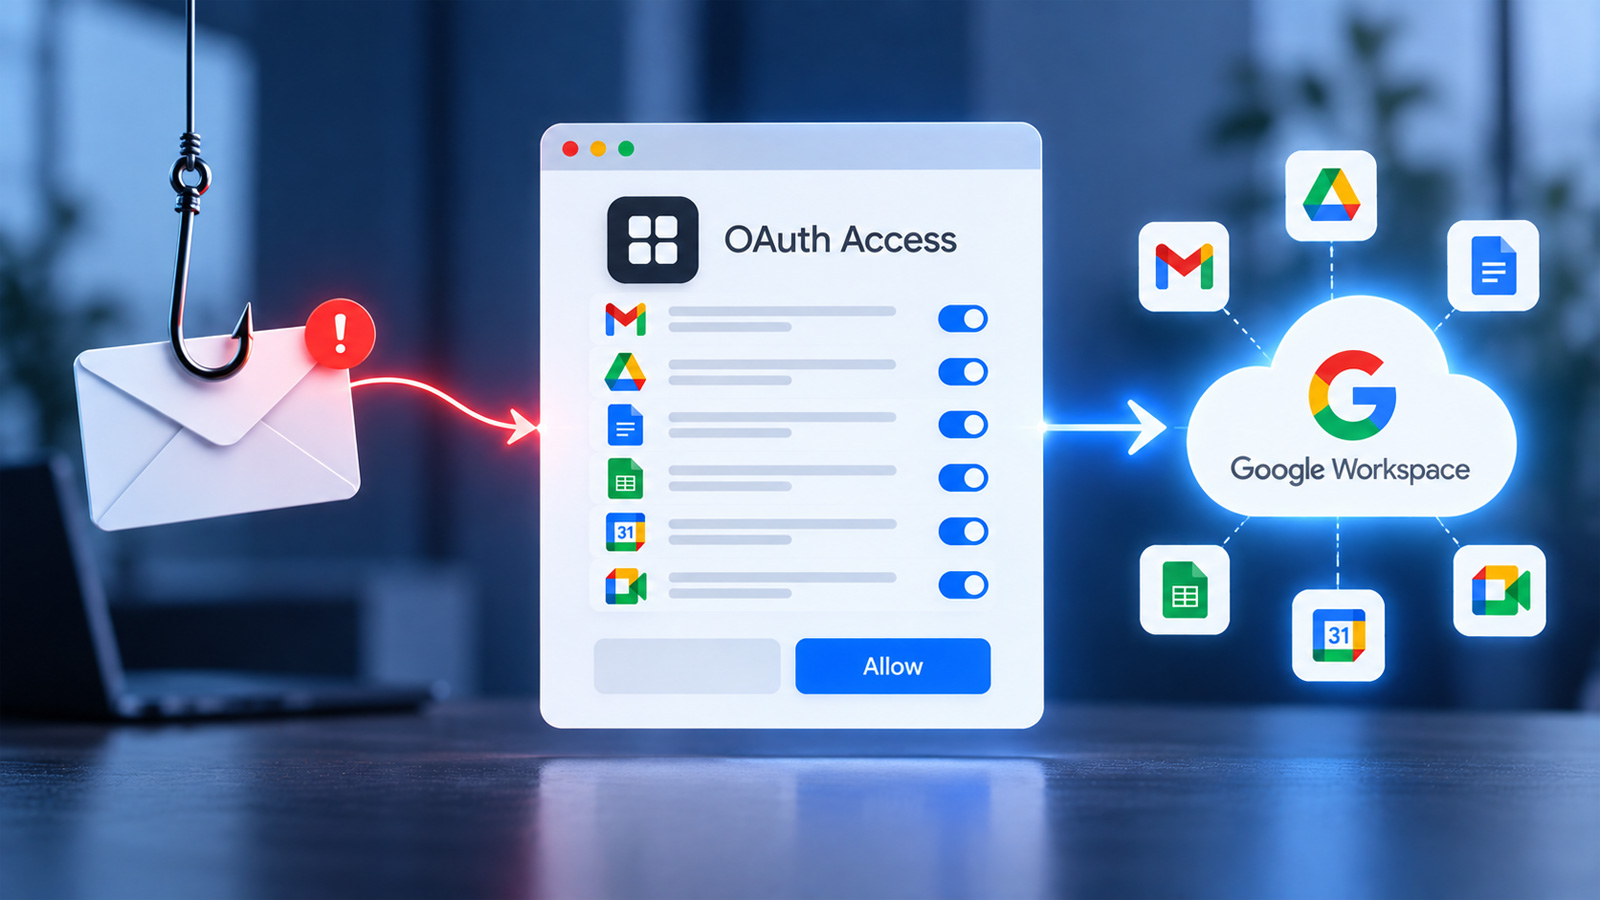
Google Workspace attackers don't necessarily need to exploit a software vulnerability or steal a user's password to gain access to an organization's data.
On September 23, 2026, BleepingComputer will host a live webinar titled "Breach autopsy: How fast-growing companies are breached through Google Workspace" with Material Security.
The webinar will feature Rajan Kapoor, Vice President of Security at Material Security, and Rick Fitzgerald, President of Fireside Consulting LLC, examining two attacks that used malicious OAuth applications and social engineering to breach Google Workspace environments.
OAuth allows users to grant applications access to Google Workspace data and services without sharing their passwords. While this makes it easier to connect legitimate applications to Google Workspace, attackers can also abuse the authorization process by convincing users to grant permissions to malicious apps.
Rather than stealing credentials, attackers can use social engineering to persuade a target to authorize an application, potentially providing access to sensitive information available through the permissions the user approved.
These attacks highlight why protecting Google Workspace requires organizations to look beyond passwords and traditional authentication controls and understand which applications have access to their environment.
During the webinar, the speakers will break down how the two attacks unfolded, the weaknesses that allowed them to succeed, and the decisions organizations made during the critical first hours of the incidents.
Attendees will also learn which security controls provide the greatest value for fast-growing organizations and what the speakers would prioritize if they were building a Google Workspace security program from scratch.
When attackers convince users to grant access
Social engineering attacks are often associated with tricking users into revealing passwords or other credentials. Malicious OAuth apps provide attackers with another approach: convincing the victim to authorize access instead.
A user may believe they are connecting a legitimate application or responding to a trusted request while actually granting a malicious app permissions within their Google Workspace environment.
The resulting access depends on the permissions granted, but the attack demonstrates why organizations need visibility into third-party applications and the access users are allowed to authorize.
By examining two attacks that combined malicious OAuth applications with social engineering, this webinar will provide a practical look at how these breaches happen and what defenders can do to reduce their exposure.
The upcoming webinar will cover:
- How attackers combine social engineering and malicious OAuth applications to target Google Workspace environments
- How users can be manipulated into authorizing application access
- What happens during the first hours of a Google Workspace breach and which response decisions matter most
- Which security controls provide the greatest value for fast-growing companies with limited security resources
- Practical security improvements organizations can implement quickly, ranked by effort and potential impact
Join us to see how malicious OAuth applications and social engineering can lead to Google Workspace breaches and what organizations can learn from real-world attacks.



 English (US) ·