The University of New Mexico Health Sciences Center disclosed a cyberattack that caused system outages and disrupted patient care and academic activities.
On Monday, UNM Health, the university’s healthcare provider, began temporarily limiting new patient admissions, diverting ambulances to nearby hospitals, and suspending outpatient surgeries and appointments.
In an update on the incident, UNM said UNM Hospital and Sandoval Regional Medical Center remain open, and all clinics will resume scheduled appointments and procedures starting today, Tuesday, October 27.
Regarding emergencies, the healthcare organization advised that people should call 911.
However, today’s classes at its four health sciences schools are canceled, and nonessential HSC employees were instructed to stay home.
UNM Health is a major statewide provider of specialist care with more than 1 million patient visits annually.
Its flagship UNM Hospital in Albuquerque houses New Mexico’s only Level I trauma center, treating the most seriously injured patients.
Byod ransomware claims the attack
UNM did not disclose the type of cyberattack it suffered, but BleepingComputer found that a new ransomware group called Byod had claimed the attack.
In a post on their data leak site, the threat actor said it had compromised 36,000 systems across UNM’s main campus and hospital environments, including Active Directory forests, Group Policy infrastructure, the entire Microsoft Entra tenant, and two Oracle databases.
"This is your entire network and infrastructure compromised, the entire university COMPLETELY," the threat actor said.
They claim access to student and employee personal data, including:
- Social Security numbers (SSNs)
- HR, payroll, and Banner student records
- Internal emails
- Research data
- Hospital appointment data
- Patient information
- Cerner EHR rosters
In an attempt to force a payment, Byod ransomware said it would take down the breach post after the university initiated communication, likely for negotiating a ransom.
BleepingComputer has reached out to UNM Health Sciences with a request for comment about these data theft allegations, but we have not received a response.
In a new post today, Byod ransomware said it would provide free keys that decrypt locked systems at healthcare facilities.
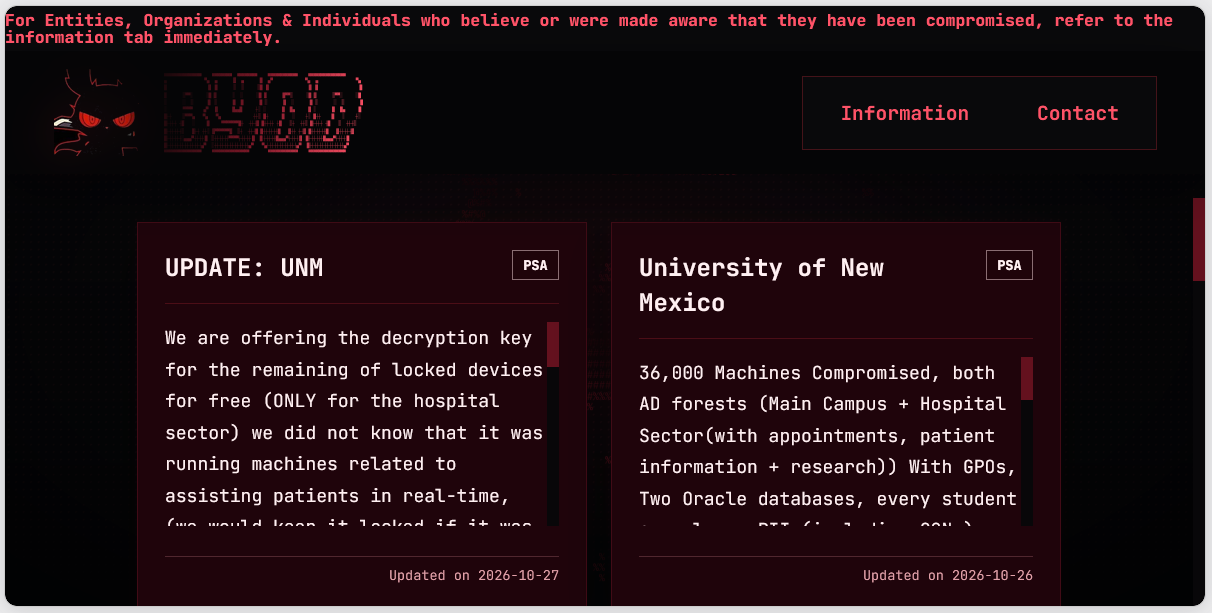 Caption
Furthermore, the threat actor promised to pay up to $2,500 for every patient affected by the cyberattack.
"We have morals and we have a heart, we are not villains, but we will still continue to hold companies responsible for bad security leading to the compromise of any customer data," the cybercriminals said.
However, the threat actor also said that it would keep all the stolen data.
Byod is a new ransomware gang that currently lists six victims on its data leak site. For three of them, it has already leaked the allegedly stolen data.
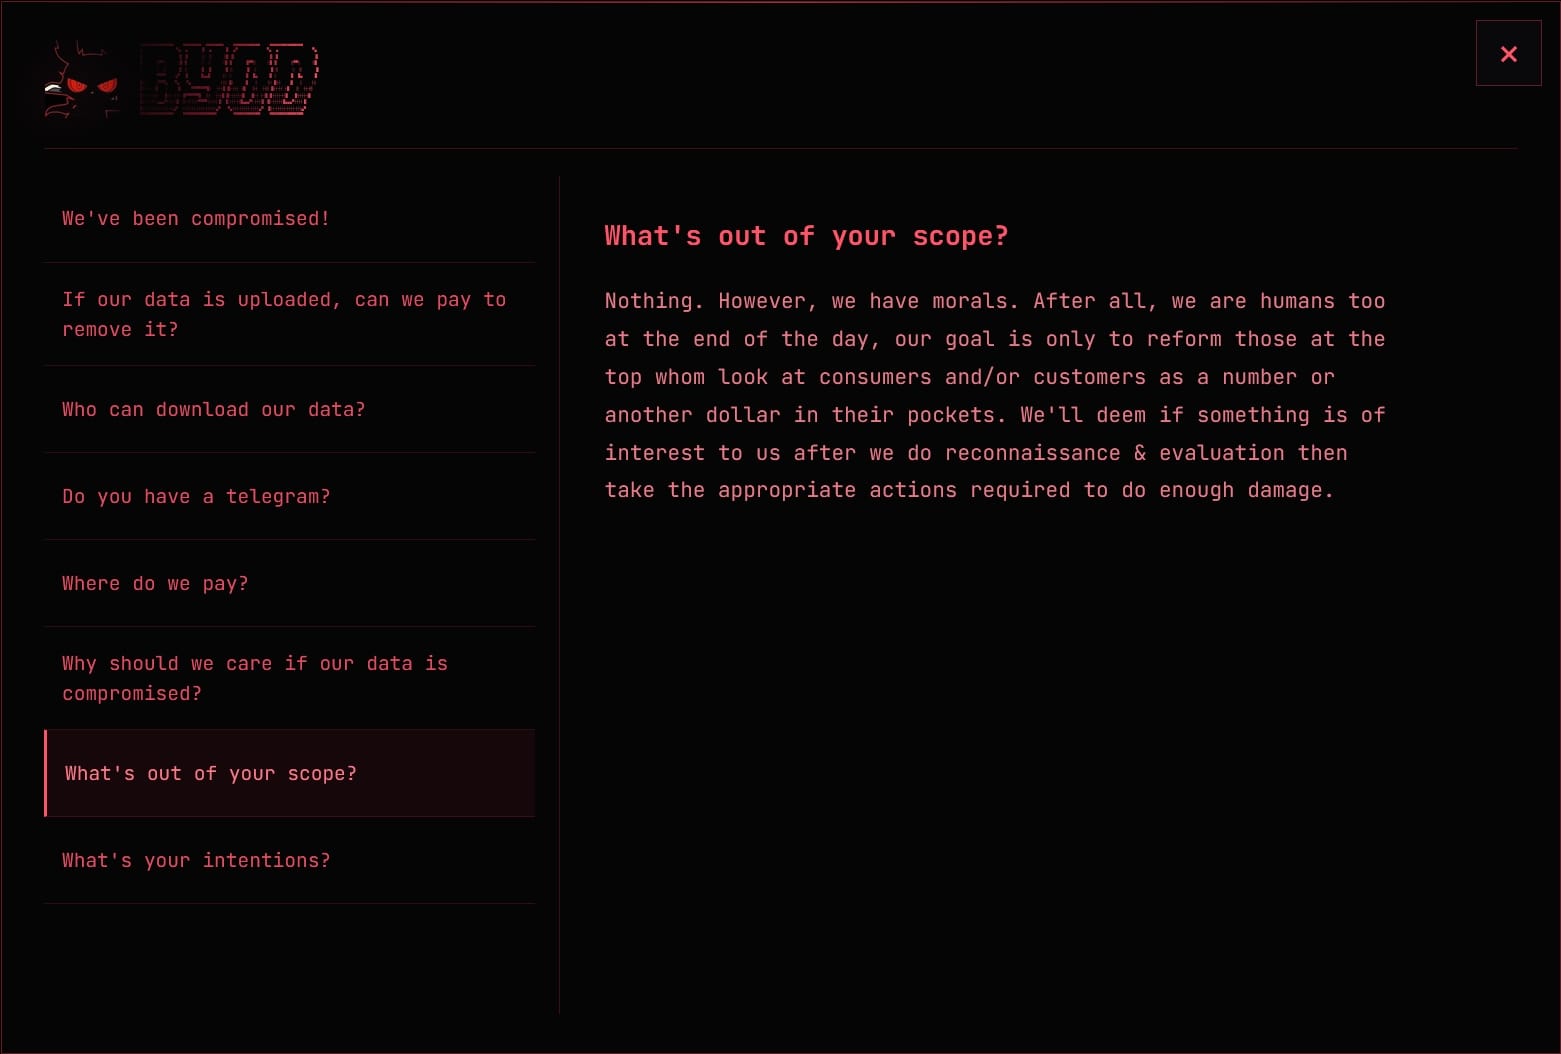
On its FAQ page, the threat group claims it is doing “pentesting” to expose vulnerabilities and hold data controllers accountable for breaches.
 Source: BleepingComputer
Byod says no target is off-limits, but it selects victims after an initial assessment identifies a target of interest. The group says it focuses on “those at the top who look at consumers and/or customers as a number or another dollar in their pockets.”
The UNM Health Sciences said today that all its critical electronic systems are back online and all UNM Health hospitals are fully open. Ambulance traffic is now operating normally, and all clinics have resumed scheduled appointments and procedures.
The university said the quick recovery was possible due to IT security teams working "with external partners to secure the network."
"Their assessment determined that the event affected some end-user devices but did not penetrate core systems or servers," UNM Health Sciences Center notes.
Patients who received care at UNM hospitals, as well as staff and students who work and study there, are advised to remain vigilant for unsolicited communications and phishing attacks.

Once attackers have valid credentials, only 37% of their actions are blocked
Overall prevention scores can hide what happens after initial access. Once attackers are using valid credentials, prevention drops sharply.
The Blue Report 2026 measures defenses technique by technique across 338 million simulations run in customer production environments.


 English (US) ·