
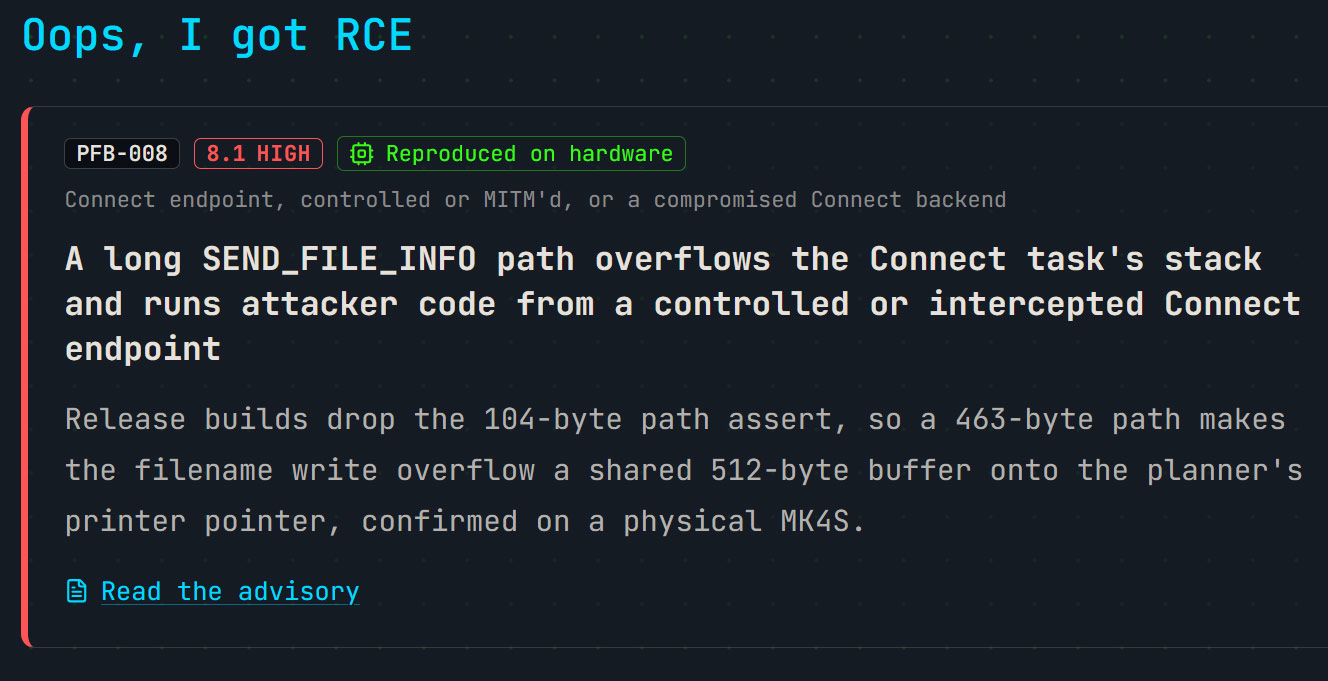
Software engineer Yannick Dixken spent a week attacking his Prusa MK4S 3D printer in the name of science. At the end of the relatively short but intense period, he produced a video demonstrating the ability to Rickroll the printer via remote code execution (RCE). Dixken shared the video and findings – charting “roughly 23 individual defects” with Prusa and published his amusing but detailed Never gonna print you up! blog in coordination with the 3D printer maker. Yes, all the vulnerabilities are now patched in the Buddy firmware versions >7.0.0.
Software engineer Rickrolls his Prusa 3D printer via remote code execution exploit
 1 week ago
33
Related
Popular

The Binding of Isaac Dev Removes Undisclosed AI-Generated Mu...
19 hours ago
68

Roosevelt's Own Book Printed a Wider Take of the Famous Roug...
21 hours ago
62

10 Most Action-Packed K-Dramas Ever Made, Ranked
23 hours ago
54
Meta Platforms commits up to $145B to AI as its ad machine k...
15 hours ago
52
 English (US) ·
© WorldNL Magazine 2026. All rights are reserved