
The developers of Goddess of Victory: NIKKE have confirmed that hackers tampered with the game's PC launcher scripts in a supply-chain attack, distributing malware capable of stealing credentials and cryptocurrency wallet data.
According to a notice published on X, a client update was issued on November 4 at 02:30 (UTC +9) to address the issue.
"We have identified an issue indicating that the PC Launcher's script files may have been tampered with by a third party," reads the statement on X.

"Accordingly, client fixes and an update were implemented on November 4 at approximately 02:30 (UTC+9). We are currently investigating the scope of the impact caused by this issue, and we will provide further details regarding follow-up measures in a separate notice."
Goddess of Victory: NIKKE is a popular sci-fi shooter RPG developed by the South Korean firm Shift Up for Windows, iOS, and Android.
Its publisher, Level Infinite, reported more than 45 million downloads since its launch in 2022, while Google Play alone reports 10 million downloads.
Malicious launcher scripts delivered backdoor
Although Level Infinite has not disclosed many details, a report on GitHub by independent security researcher MotherSphere alleges the incident involved four JavaScript files hosted on Level Infinite's official content delivery network (CDN).
According to the researcher, the files were modified on September 27, 2026, to inject malicious JavaScript that downloaded additional code from attacker-controlled servers whenever players opened the game launcher.
The injected code was hidden within legitimate JavaScript files and used obfuscation to conceal the domains insightjs[.]com and insightjs[.]org, from which the malicious code was downloaded.
BleepingComputer examined two of the modified JavaScript files and confirmed that they contained an obfuscated loader designed to retrieve and execute additional code from these domains, falling back to the second domain if the first was unavailable.
According to MotherSphere's analysis, the downloaded code abused the launcher's native functionality to retrieve and execute a malicious LuaJIT payload called insight.bundle, which installed a remote-access agent referred to as K2F.
The backdoor allowed attackers to remotely execute commands, browse and download local files, capture screenshots, collect NIKKE account credentials, and steal information stored in web browsers.
The malware also supported an additional command to install a malicious Windows DLL named platform_experience_helper.dll that could remain active after the game launcher was closed.
BleepingComputer analyzed strings extracted from a DLL sample uploaded to VirusTotal and found code indicating that the malware can steal cryptocurrency wallet data from browser extensions, including MetaMask, Phantom, Coinbase Wallet, and others.
The DLL contained functionality to intercept sensitive wallet information, including recovery phrases and private keys, potentially allowing attackers to steal cryptocurrency.
However, it is unknown whether the attackers deployed this additional component on infected systems or successfully stole cryptocurrency from players.
The researcher claims that Level Infinite replaced three of the impacted JavaScript files on November 3 with clean versions. However, they claim a tampered copy of the fourth was reportedly still being served to users as of 22:26 GMT.
This suggests that at least one compromised script may have remained accessible after the company deployed its client update.
The researcher also shared indicators of compromise (IOCs) that users can check to determine whether the malicious Lua agent executed on their computers.
One indicator is the string k2f_chan registered in the Launcher/intl_service/debug.log file within the NIKKE installation directory.
This entry indicates the malicious Lua agent executed, but it does not confirm whether the DLL was loaded as well.
BleepingComputer also found that the insightjs[.]org backup domain is now serving code that displays a security warning inside the game launcher.
The warning, displayed in English, Chinese, Japanese, and Korean, tells players to immediately close the launcher and refrain from opening the PC client until the publisher confirms the issue has been resolved.
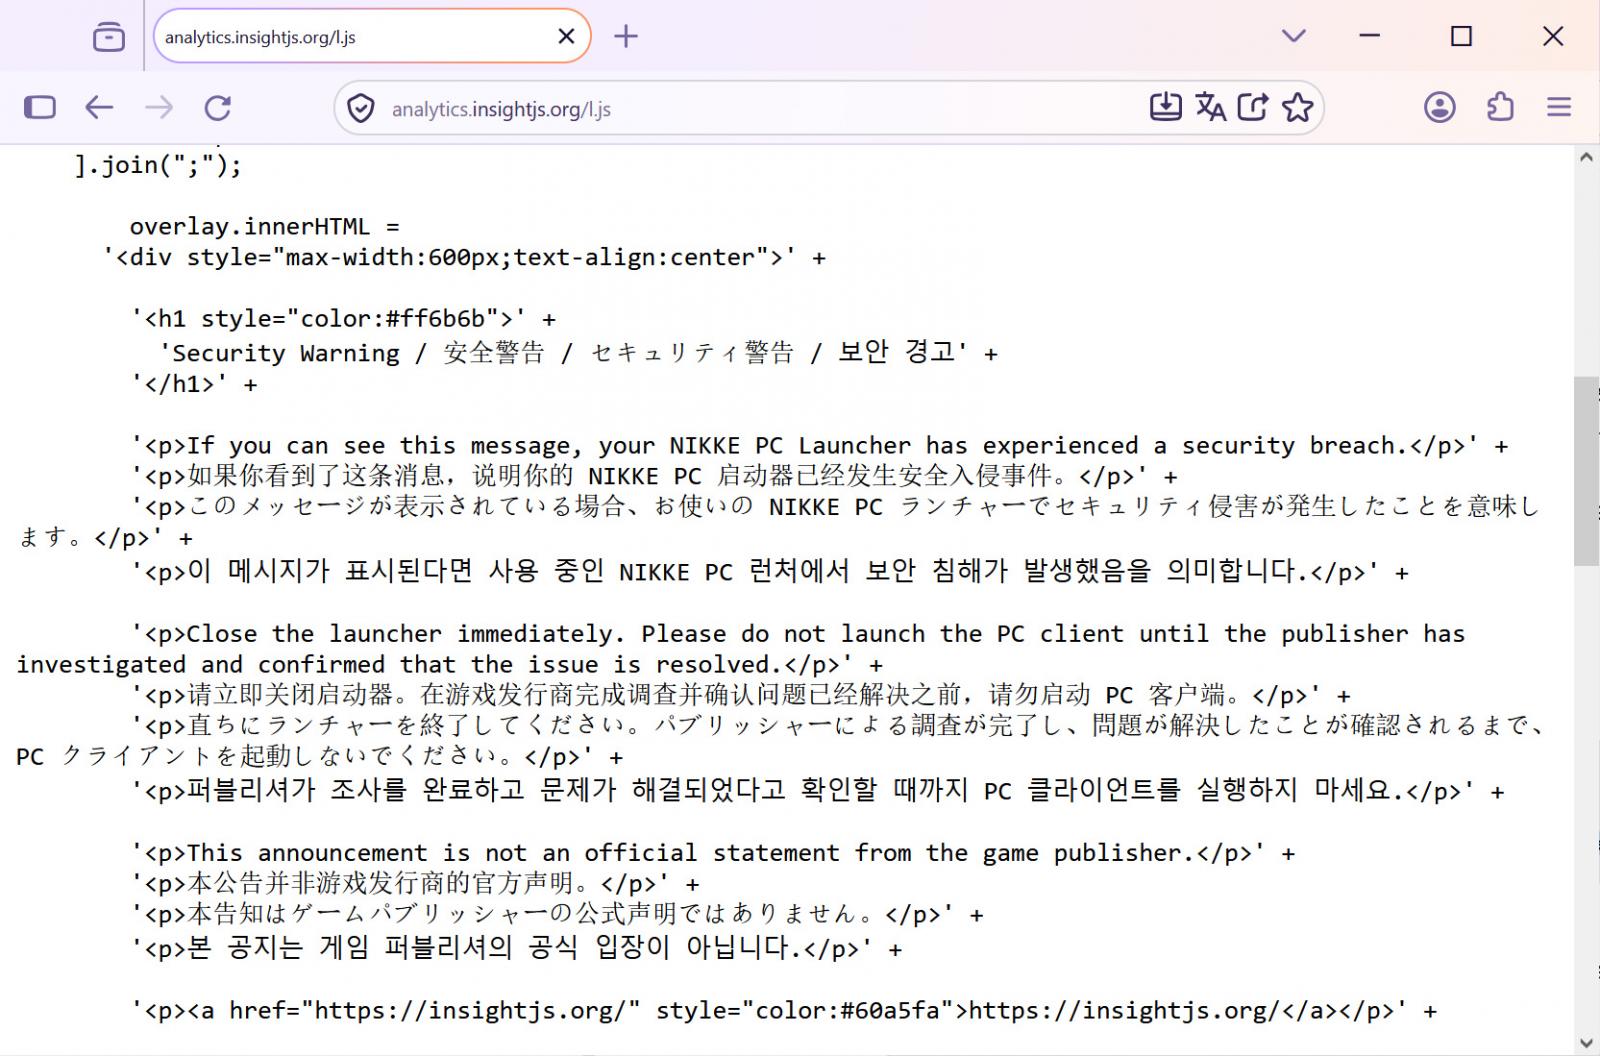 Warning about supply chain attack on attacker's backup domain
Source: BleepingComputer
The message confirms that this is not an official announcement from the game's publisher, so it unclear who currently controls the domain or when the malicious payload was replaced with the warning.
BleepingComputer has contacted Level Infinite for comment on MotherSphere's findings, but has not received a response by publication.
Potentially affected players should run a full system scan using updated antivirus software.
Those who find they were compromised should reinstall Windows, and change passwords and other sensitive credentials from a clean device.

Uncover email threats your existing defenses may miss.
Adaptive Security's AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what's getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.




 English (US) ·