
US cybersecurity company F5 warned customers to patch five BIG-IP vulnerabilities that attackers can exploit to trigger denial-of-service (DoS) or gain remote code execution.
Tracked as CVE-2026-121805, CVE-2026-120292, CVE-2026-120285, CVE-2026-116953, and CVE-2026-123637, these stack-based buffer overflow flaws affect the company's BIG-IP Access Policy Manager (APM) centralized access management proxy solution and the BIG-IP iRules programmable scripting feature.
All five security issues are rated critical severity, and unauthenticated threat actors can exploit them to execute arbitrary code remotely on unpatched systems.
The company also released engineering hotfixes for a high-severity BIG-IP APM SAML vulnerability (CVE-2026-126822) stemming from an integer underflow (wrap or wraparound) weakness that remote, unauthenticated threat actors can abuse in denial-of-service (DoS) attacks.
F5 said it has no mitigation measures for these flaws and advised security teams to install the out-of-band hotfixes released on Wednesday to address them on vulnerable devices.
Internet threat watchdog Shadowserver currently tracks more than 177,000 BIG-IP instances and over 14,600 IP addresses with BIG-IP APM fingerprints exposed online. However, there is no information on how many are honeypots or have already been patched against these vulnerabilities.
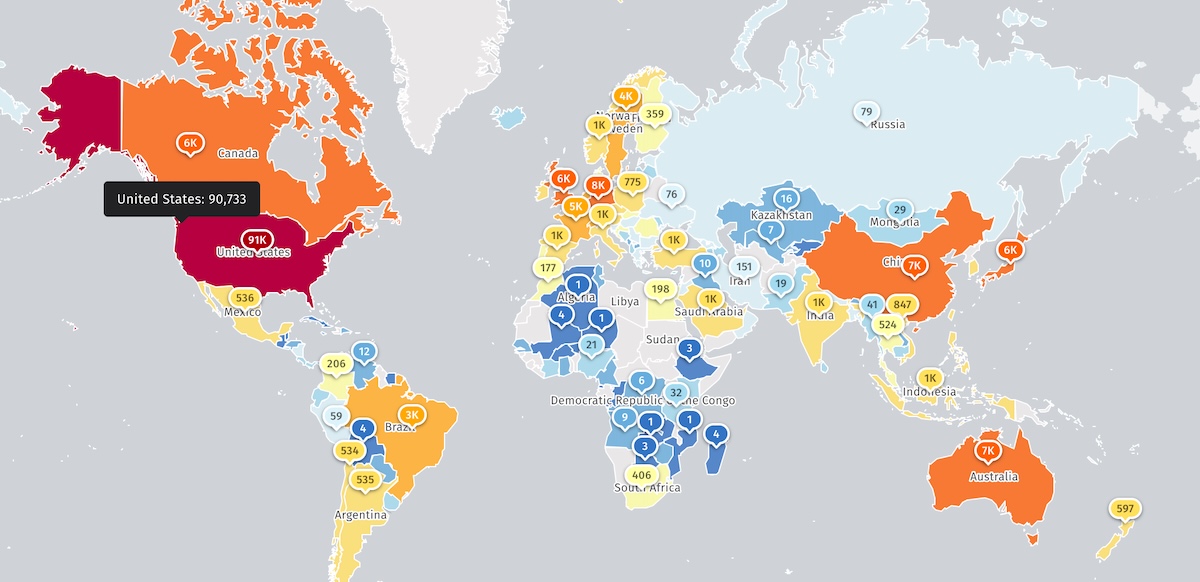 Internet-exposed BIG-IP instances (Shadowserver)
Although the company hasn't flagged any of these issues as exploited in attacks, admins should upgrade systems to the latest version as soon as possible, since cybercrime and nation-state threat groups have often abused F5 vulnerabilities in the wild.
Attackers have targeted F5 security flaws to breach corporate networks, map internal servers, hijack devices, deploy data-wiping malware, and steal sensitive files from victims worldwide in recent years.
The US Cybersecurity and Infrastructure Security Agency (CISA) has flagged seven F5 vulnerabilities as actively exploited since November 2021, four of them also used by ransomware gangs.
Most recently, in September, F5 also patched a critical BIG-IP APM vulnerability (CVE-2026-94127) that is being actively exploited in zero-day remote code execution attacks.
One year ago, F5 also disclosed that state-backed hackers breached its systems in August 2025 to steal source code and information on undisclosed BIG-IP security vulnerabilities.
F5 is a Fortune 500 tech company that provides cybersecurity, application delivery networking (ADN), and other services to more than 23,000 customers, including 80% of the Fortune Global 500 and 48 of Fortune 50 companies.

Uncover email threats your existing defenses may miss.
Adaptive Security's AI agents analyze email intent, context, and behavior to uncover phishing, business email compromise, and invoice fraud.
See what's getting through with a 14-day read-only scan of Microsoft 365 or Google Workspace, with no MX changes.


 English (US) ·